A company that fails to plan, plans to fail.
Every regulated company is having the same conversation right now. The board wants an AI strategy. Employees want better tools. Compliance wants to know where the data goes. Security wants to know who approved it. Somewhere in the middle, a small team is told to “roll out AI” with a license budget, a deadline, and very little else.
Most of those rollouts will stall. Not because the technology doesn’t work, but because the organization treated AI as a software purchase instead of an operating change. In a firm where every client communication is a record, every data flow is auditable, and every new vendor is a risk assessment, that mistake costs more than it would anywhere else.
This article covers where companies usually go wrong, the moments when they give up, and what a thoughtful implementation looks like instead.
The numbers are not encouraging
The research on enterprise AI adoption tells a consistent story: lots of pilots, little production.
- MIT’s NANDA initiative reported in The GenAI Divide: State of AI in Business 2025 that roughly 95% of generative AI pilots stall before reaching scaled adoption. Critics have questioned how that figure was calculated, but the direction matches other studies.
- Gartner found that at least half of generative AI projects were abandoned after proof of concept by the end of 2025, citing poor data quality, inadequate risk controls, escalating costs and unclear business value.
- S&P Global Market Intelligence found the share of companies abandoning most of their AI initiatives before production jumped from 17% to 42%, with the average organization scrapping 46% of its proofs of concept.
Notice what appears in Gartner’s list: inadequate risk controls. For a regulated company, that isn’t one failure point among many. It’s the one that ends the program.
Meanwhile, the people the program was supposed to serve aren’t waiting. Surveys in 2025 found roughly half of workers using AI tools their employer never approved, and in one study three-quarters of those users admitted sharing potentially sensitive information such as customer data, employee details and internal documents. Senior leaders were among the heaviest users. IBM has estimated that shadow AI adds about $670,000 to the average cost of a data breach.
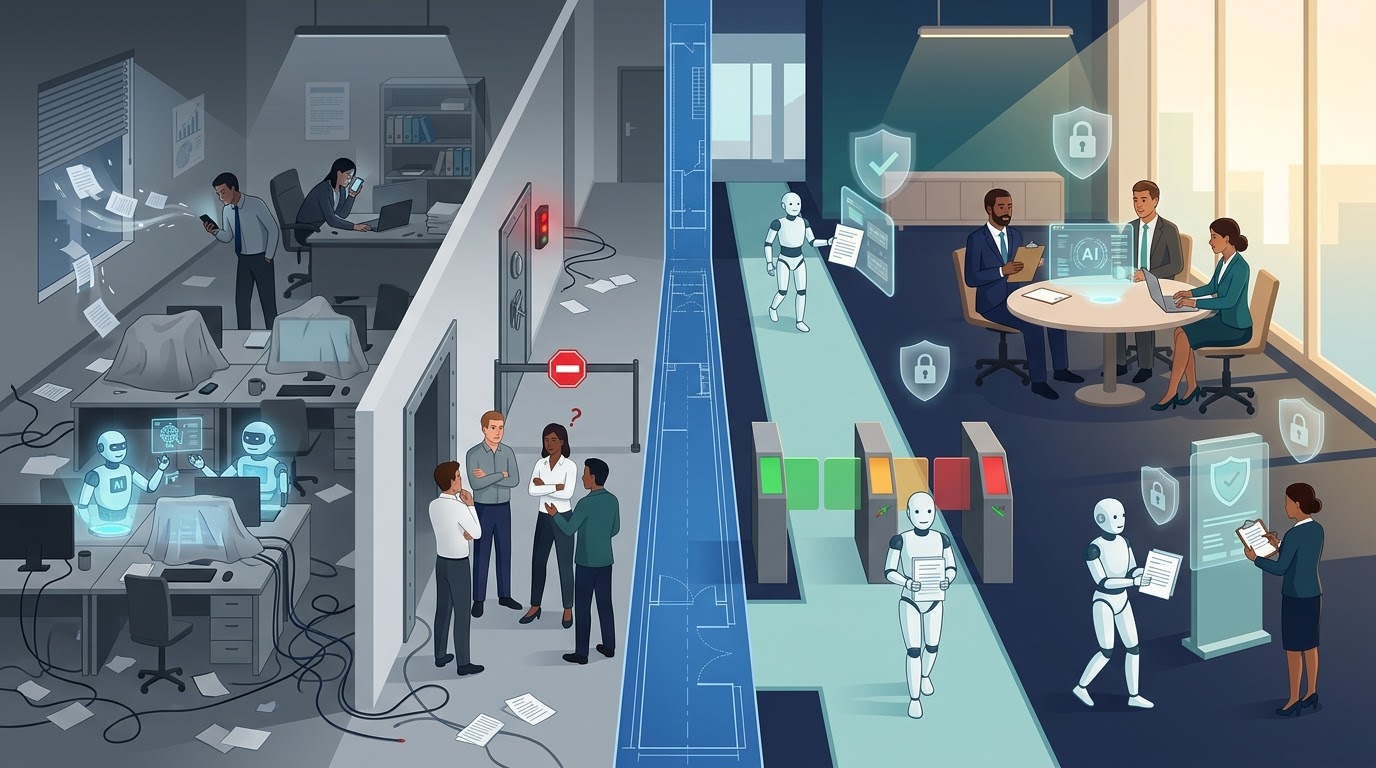
That’s the real choice in front of a regulated company. It isn’t “AI or no AI.” It’s governed AI or ungoverned AI.
Where most companies go wrong
1. They start with the tool, not the problem
The most common opening move is buying licenses: an enterprise chat assistant, a copilot bundle, a platform trial. Then the team goes looking for things to use it on. Without a defined business problem, there’s no baseline, no success metric and no way to answer the question every CFO eventually asks: what did we get for this?
2. They treat compliance as the last gate instead of the first partner
In many rollouts, compliance and security see the project for the first time when it’s nearly finished. They’re handed a working demo and asked to sign off. Of course they say no, or “not yet,” because nobody can answer their questions: Where is the data stored? Is it used for model training? How are outputs retained? Who supervises AI-drafted client communications? What happens when it’s wrong?
The project team then calls compliance “the department of no,” and the relationship never recovers.
3. They pick a side of the ban-or-buy binary
Some firms ban AI outright. Others buy a tool and turn it on for everyone. Both fail in regulated environments. Bans don’t stop usage, they push it onto personal phones and free accounts where the firm has zero visibility. Open-door rollouts without data rules invite exactly the incident the ban was trying to prevent.
4. They ignore the data underneath
AI is only as safe and as useful as the data it can reach. Companies that haven’t classified their data, cleaned up permissions or decided which systems AI may touch end up with one of two outcomes: an assistant that can see far more than any single employee should, or an assistant locked down so tightly it can’t do anything useful.
5. They run pilots with no path to production
A pilot without predefined exit criteria is a demo with a calendar. Teams run a few weeks of experiments, collect enthusiastic anecdotes, and then discover there’s no budget, no owner and no approved architecture to take it further. This is “pilot purgatory,” and it’s where most of those abandoned proofs of concept live.
6. They treat training as a one-time event
A single lunch-and-learn doesn’t change how people work. Neither does a policy PDF nobody reads. Adoption in regulated firms requires role-specific training that covers both how to use the tools and what not to put in them, reinforced over time.
Where they give up
AI programs rarely die in one dramatic moment. They erode at predictable pressure points:
- The first hard “no” from compliance or security. Leadership hears “risk” and decides to pause indefinitely, rather than asking what controls would turn the no into a yes.
- The first visible mistake. An AI-drafted summary contains an error, or a hallucinated detail reaches a manager. With no human-review step designed in, the reaction is to pull the tool rather than fix the process.
- The first real invoice. Usage-based costs climb, and nobody budgeted for the full cost of ownership: integration, monitoring, training and support.
- The first budget review. Without baseline metrics, nobody can prove value. Anecdotes lose to spreadsheets.
- The champion leaves or loses support. When AI lives inside one enthusiastic person instead of a governed program, it walks out the door with them.
Every one of these is foreseeable. Which means every one of them can be planned for.
What to do instead
Build the governance before you buy the licenses
Stand up a small AI working group with real authority: a business owner, compliance, information security, legal, IT and a handful of end users. Give it a charter. Its job isn’t to slow things down, it’s to make decisions quickly and consistently so that each new use case doesn’t restart the debate from zero.
The first deliverable is an acceptable-use policy written in plain language: what tools are approved, what data can go into them, what requires human review, and who to ask when something isn’t clear.
Classify your data and tier your use cases
Not every use case carries the same risk. Sort them into tiers before anyone builds anything:
| Tier | Examples | Controls |
|---|---|---|
| Green (low risk) | Drafting internal docs, summarizing public research, brainstorming, code help on non-production systems | Approved enterprise tool, no client or confidential data, standard logging |
| Yellow (moderate) | Summarizing internal meetings, drafting client-facing content, analyzing internal operational data | Approved tool with data-retention controls, mandatory human review before anything leaves the firm, records retained |
| Red (high risk) | Anything touching client PII, account data, investment recommendations, trading, HR decisions | Formal risk assessment, compliance sign-off, documented supervision, audit trail, explicit owner |
Start in green. Earn your way into yellow. Treat red as a separate project with its own review.
Bring compliance in at design, and write the supervision story
Regulators won’t ask whether you use AI. They’ll ask how you supervise it. Before a use case goes live, be able to answer:
- What data does this touch, and where does it go?
- Is the vendor contractually barred from training on our data?
- How are prompts and outputs logged and retained?
- Who reviews outputs before they reach a client or a regulator?
- How do we detect and correct errors?
- How do we turn it off?
If you design those answers in from the start, compliance becomes a co-author of the solution rather than a reviewer of someone else’s. That shift alone changes most “no” answers to “yes, with these conditions.”
Make the sanctioned path easier than the shadow path
The cure for shadow AI isn’t a stricter ban. It’s an approved tool that’s good enough that people stop reaching for their personal accounts. Provide an enterprise-grade option with single sign-on, data protections and logging, then pair it with monitoring that tells you where unapproved usage is still happening. Use that signal as demand data: it shows you which use cases people care about most.
Pick a few boring, measurable use cases
The best first projects are unglamorous: meeting summaries, first drafts of internal reports, policy lookup, ticket triage, document comparison. They’re low-risk, high-frequency and easy to measure. Before the pilot starts, record the baseline: how long the task takes today, how often it’s done, what errors occur. Then define what success looks like in numbers.
Define the exit gates before the pilot begins
Every pilot should launch with three things written down: the success criteria, the owner who will run it in production, and the budget and architecture that production will require. At the end of the pilot, the decision is mechanical: it met the criteria and scales, it missed and gets adjusted, or it failed and gets retired. All three are acceptable outcomes. Drifting is not.
Design humans into the loop
Human review isn’t a sign that the AI isn’t good enough. In a regulated firm, it’s a feature. Build review steps into the workflow itself, so a reviewer approves a draft before it’s sent rather than catching problems after. That also gives you the audit trail regulators will want to see, and it means the first inevitable mistake becomes a caught error instead of an incident.
Budget for the whole cost
Licenses are the smallest line item. Plan for integration work, security review, monitoring, training, support and usage growth. A program that’s honest about cost on day one doesn’t get ambushed at the first budget review.
Train by role and keep training
An advisor, an operations analyst and a developer use AI differently and face different risks. Train them differently. Build a small network of champions in each department who can answer questions and share what’s working. Refresh the training as the tools and policies change, because they will.
Measure, report and iterate
Publish a simple monthly scorecard: adoption, time saved against baseline, issues caught by human review, incidents, and shadow-AI trends. This is what keeps leadership support through the inevitable bumps. It replaces “we think it’s helping” with “here’s what it did.”
A practical 90-day starting plan
| Phase | Focus | Outcomes |
|---|---|---|
| Days 1–30: Foundation | Governance and guardrails | AI working group chartered; acceptable-use policy published; data classification and use-case tiers defined; one approved enterprise tool selected and vetted |
| Days 31–60: Prove | Two or three green-tier pilots | Baselines recorded; success criteria and owners named; role-based training delivered; logging and review steps live |
| Days 61–90: Scale or stop | Decide with data | Pilot results reported against criteria; winners moved to production with budget; first yellow-tier use case scoped with compliance; monthly scorecard established |
Ninety days won’t transform a company. It will give you something most firms never build: a repeatable, defensible way to say yes to AI.
Plan to succeed
The companies that get AI right in regulated industries won’t be the ones that moved fastest. They’ll be the ones that moved deliberately, with compliance at the table, data under control, humans in the loop and metrics that prove value. The technology is ready. The question is whether the organization is.
A company that fails to plan, plans to fail. A company that plans well gets to keep going when everyone else gives up.
Sources
- MIT report: 95% of corporate generative AI pilots fail to deliver returns (Computing)
- MIT report flags 95% GenAI failure rate, but critics say it oversimplifies (BigDATAwire)
- Why 50% of GenAI Projects Fail (Gartner)
- Generative AI shows rapid growth but yields mixed results (S&P Global Market Intelligence)
- Roughly half of employees are using unsanctioned AI tools (CIO)
- Managers turn blind eye to unapproved AI use (FinTech Global)